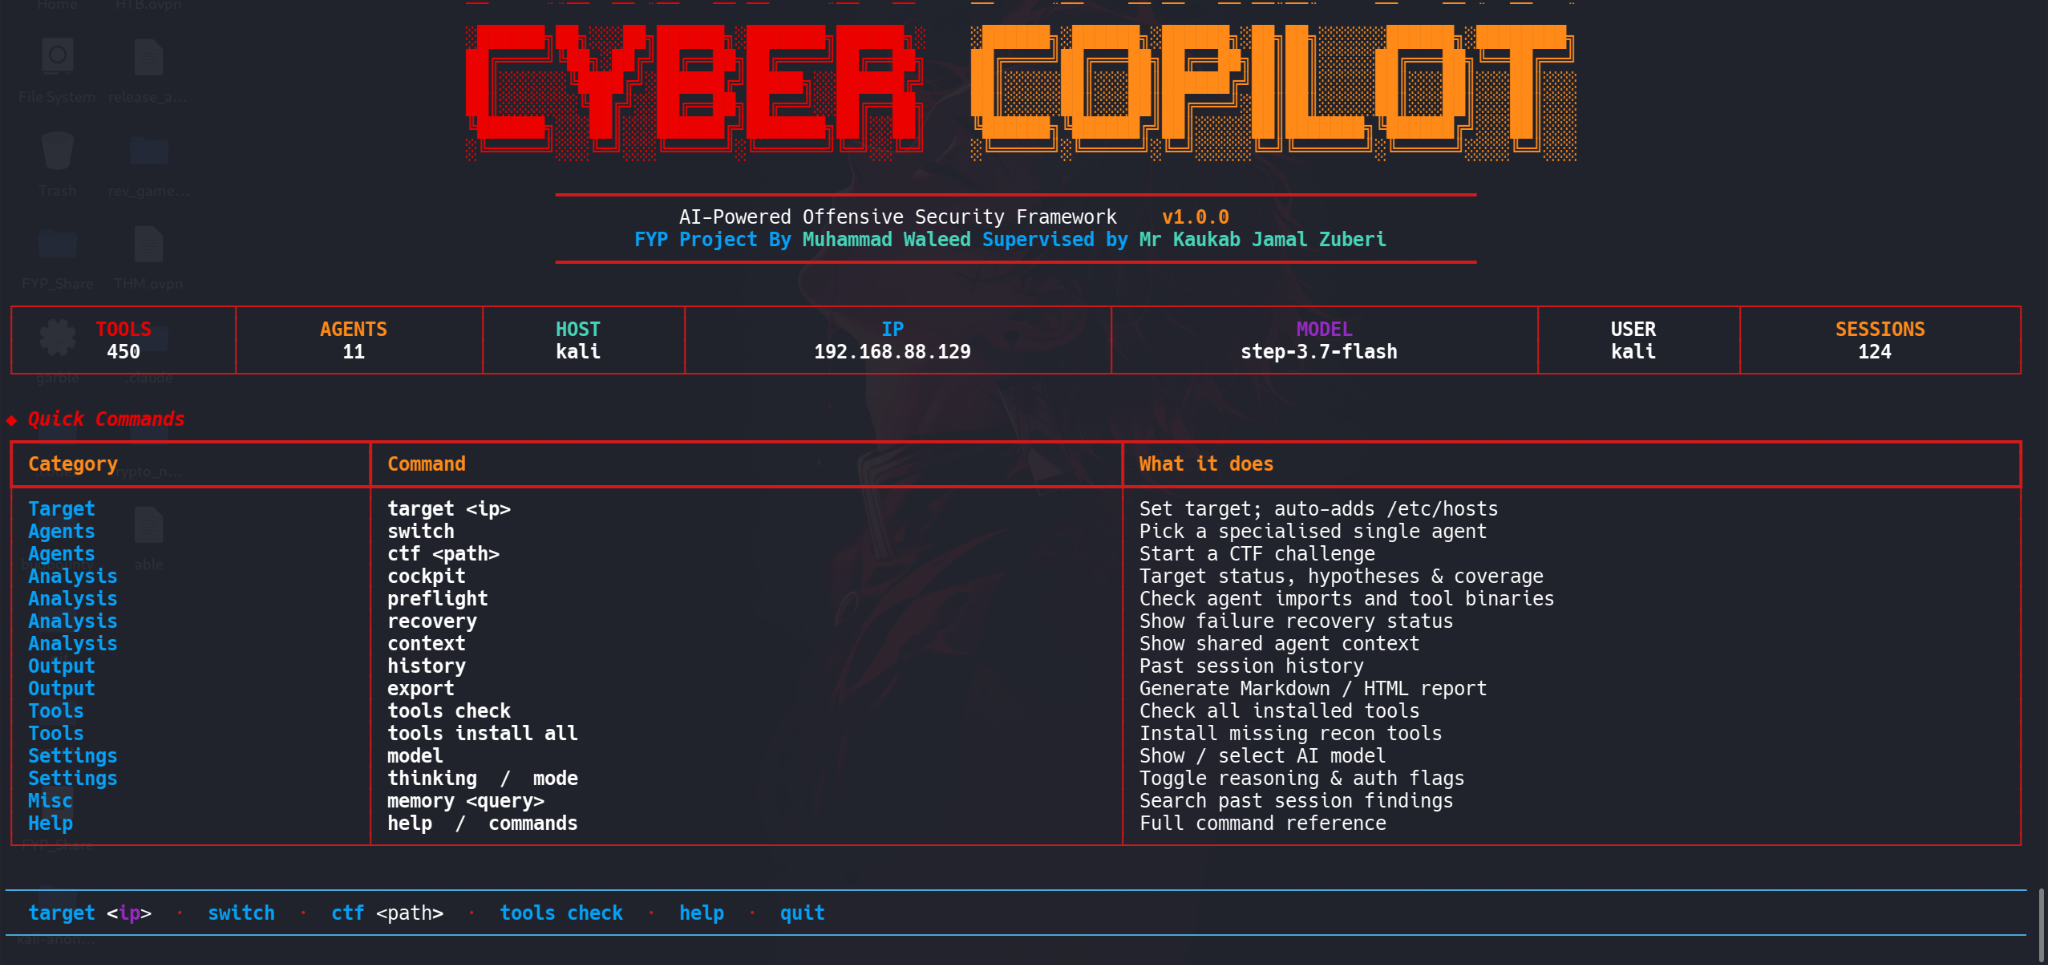
CYBER-COPILOT
Terminal-native offensive-security framework with ten specialist agents, ReAct execution, persistent target memory, seven-strategy failure recovery, human approval gates, and automated Markdown/PDF reporting.
Offensive security and Digital Forensics specialist building practical AI-assisted security systems. Cyber-CoPilot spans 149 Python modules, approximately 70,500 lines, ten specialist agents, and 60+ integrated security tools; FlagSniff applies tool-using AI and RAG to PCAP investigation. CTF team lead with two first-place finishes and one national runner-up result.
Terminal-native offensive-security framework with ten specialist agents, ReAct execution, persistent target memory, seven-strategy failure recovery, human approval gates, and automated Markdown/PDF reporting.
Python desktop PCAP-analysis platform combining automated threat detection, stream reconstruction, tool-using AI, RAG-assisted investigation, recovery controls, visualization, and report export.
Conducted comprehensive penetration testing and vulnerability assessments in a specialized research environment. Identified security flaws and provided actionable remediation strategies for organizational systems.
Performed LLM security testing including prompt injection, jailbreaking, and adversarial input analysis. Evaluated model robustness and safety boundaries to identify vulnerabilities in deployed AI systems.
Inter University Cyber Triade Battle. UCP Takra 2026 CTF Champion. Runner-Up: Cyber Battle Pakistan 2026.
Web Application Security, Vulnerability Assessment, and Penetration Testing using Burp Suite, Nmap, and Metasploit.
Evidence Acquisition, OSINT, and Binary Analysis utilizing Autopsy, FTK Imager, Wireshark, and x32dbg.
Advanced Python development, Retrieval-Augmented Generation (RAG), and NLP integration for automating security workflows.
Cyber-CoPilot is a terminal-native offensive-security framework built as 149 Python modules and approximately 70,500 lines of code. A central orchestrator routes work to ten specialist agents and exposes more than 60 MITRE-mapped security tools through transparent ReAct execution loops.
Persistent target memory prevents duplicate work; a seven-strategy recovery engine handles tool failures and blocked requests; scope enforcement and human approval gates retain operator control. Findings flow into client-ready Markdown and PDF reports with severity charts, executive summaries, and MITRE ATT&CK alignment.
Approximately 70,500 lines of Python across agents, SDK infrastructure, tool wrappers, memory, and reporting.
Specialists for recon, web security, red teaming, AppSec, bug bounty, CTF, DFIR, adversarial testing, and reporting.
Scope enforcement, visible commands, replayable logs, and approval-gated exploitation keep every action accountable.